What is SBOM Observer?
What SBOM Observer does, from importing SBOMs to vulnerabilities, policies, and sharing.
SBOM Observer imports SBOMs and related attestations (VEX, SLSA provenance) from your own builds and from suppliers, finds the vulnerabilities in the components they list, and checks them against your policies. It answers which software you run, which of it is affected by a vulnerability, and which components break your rules.
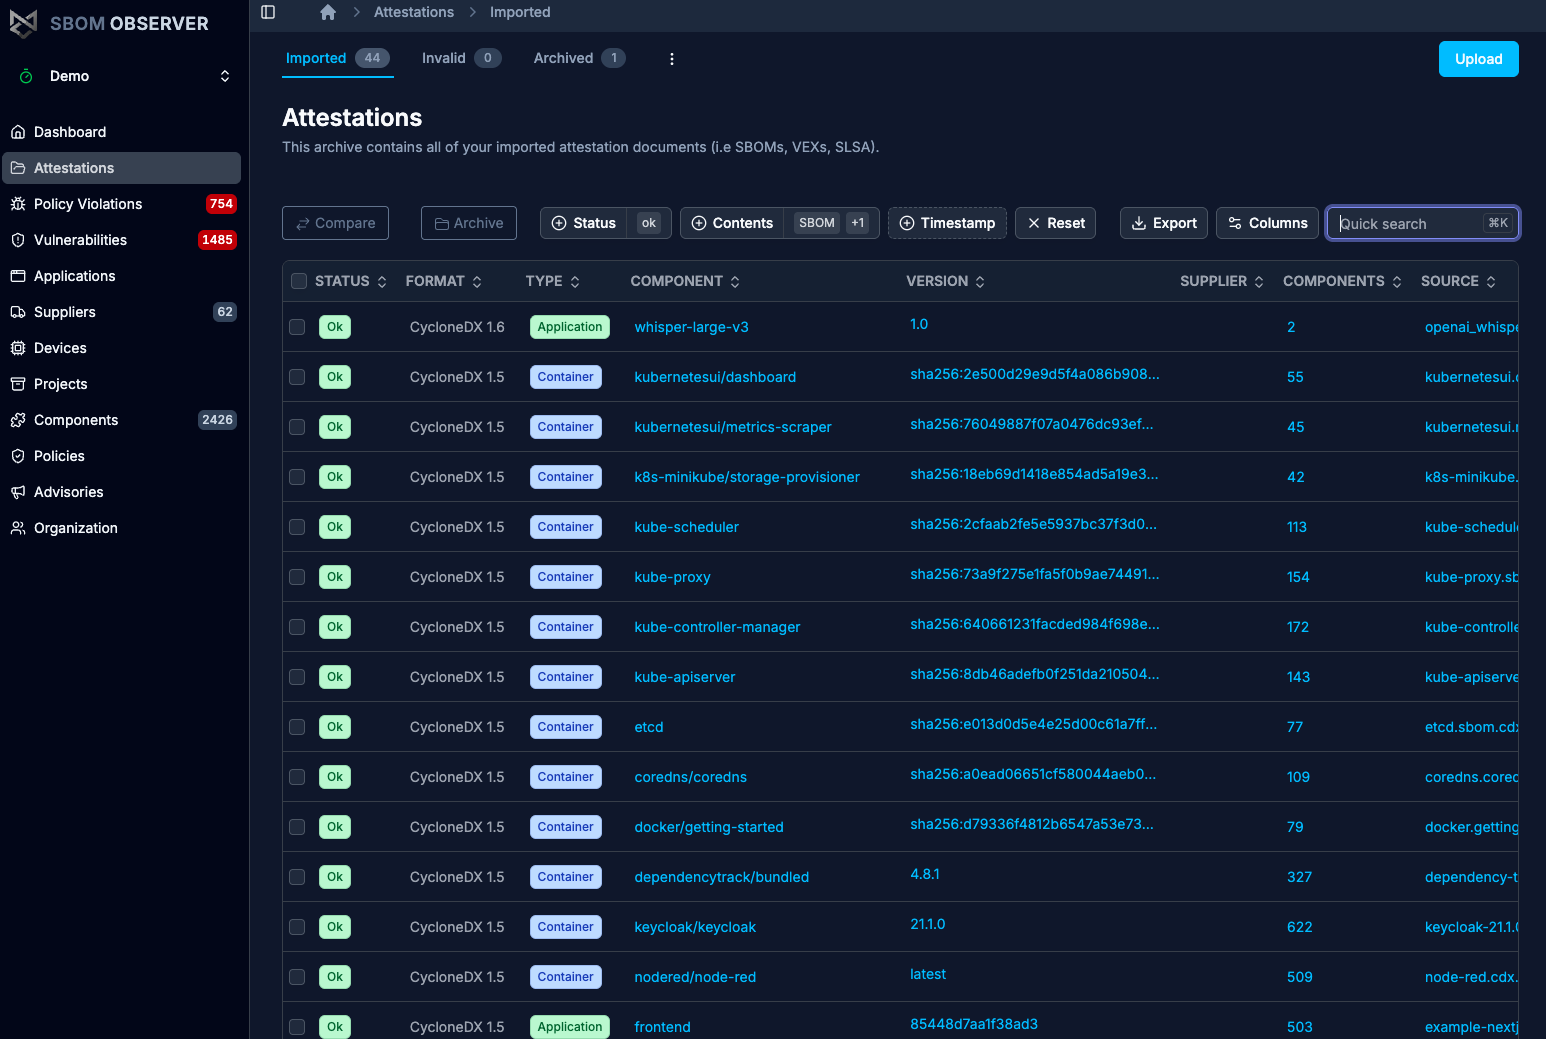
How it fits together
| Stage | What happens |
|---|---|
| Generate | Create SBOMs with the open-source Observer CLI, or import SBOMs from suppliers and other tools in CycloneDX or SPDX. |
| Analyze | Components are matched against advisory sources for vulnerabilities, and linked to suppliers and VEX analysis. |
| Enforce | Policies turn the data into violations, and the CLI can fail a CI/CD build on them. |
| Prove | The original SBOMs, the VEX analysis, and the violations stay in one place, so you can show what you knew about a component and what you decided about it. |
| Share | Export SBOMs with vulnerabilities and VEX; publish them to customers with Trust Repository. |
Who builds it
SBOM Observer is part of Bytesafe, built by Bitfront AB in Sweden. The other Bytesafe products are the Dependency Firewall, which blocks vulnerable and malicious packages at install time, and Trust Repository, which collects and publishes SBOMs and VEX between suppliers and customers.
SBOM Observer is available cloud-hosted or self-hosted, including air-gapped. See Deployment models.
Next steps
- Try the Quickstart in the live demo, no signup needed.
- Read Policies and Data model fundamentals.